Cybersecurity solutions / Caring Via Technology
Discover Vulnerabilities Before Attackers Exploit Them.
Identify security weaknesses across your organisation’s networks, business applications, servers, databases and cloud environments through structured vulnerability assessments and authorised penetration testing.
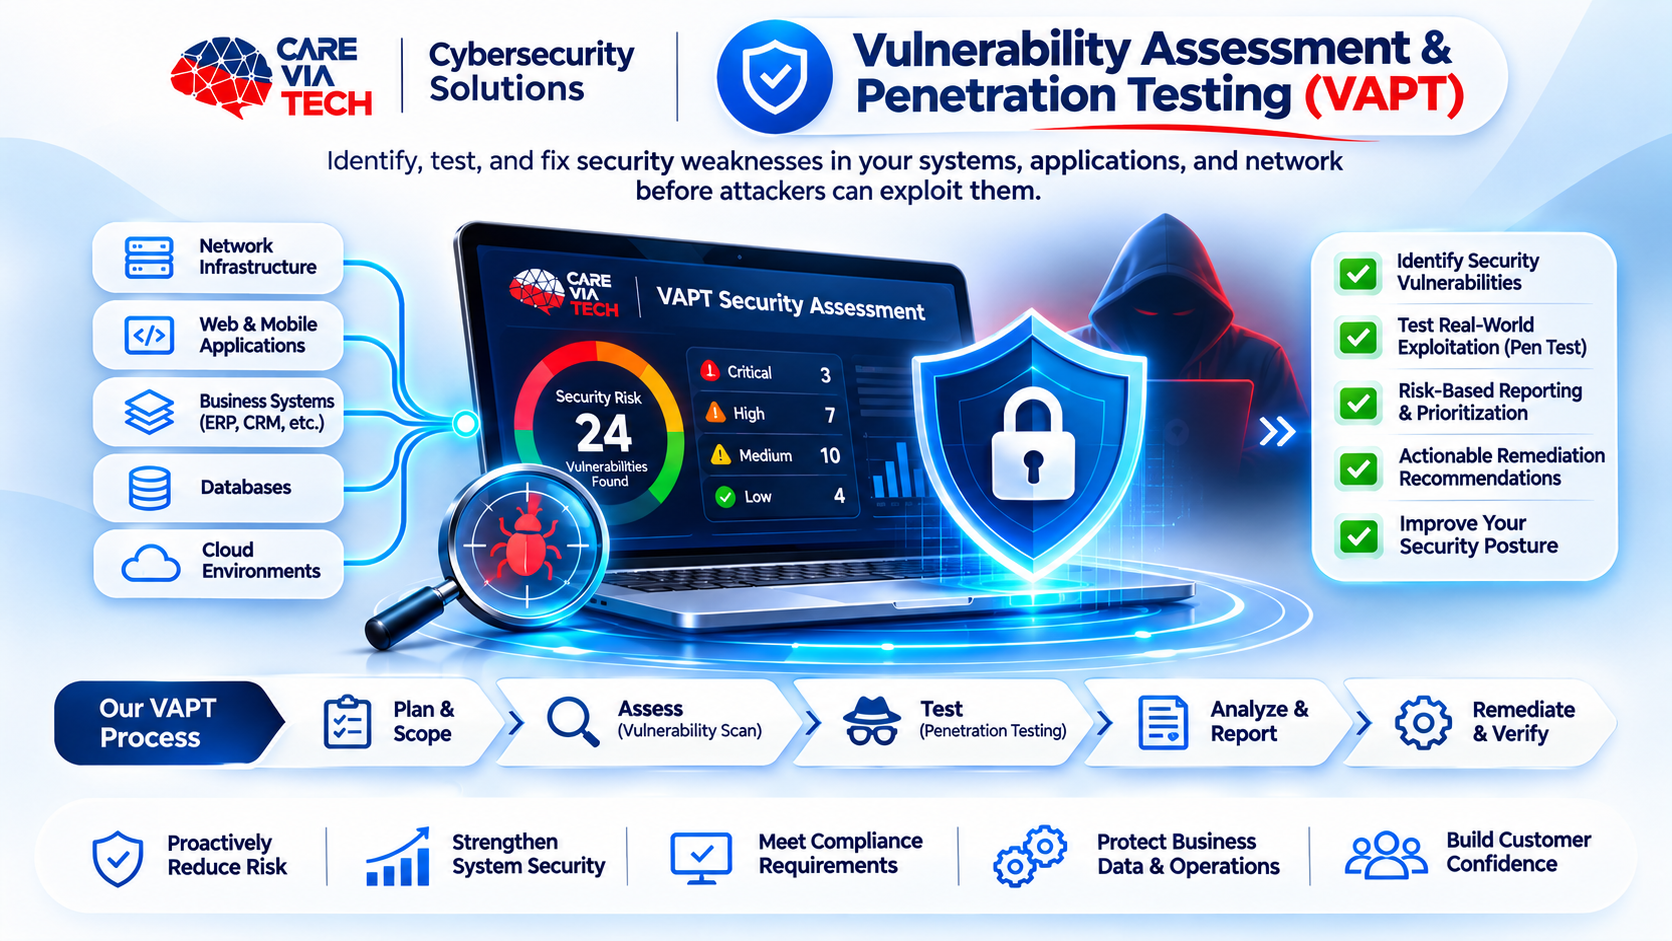
Assessment targets
Identify → Validate → Prioritise
Documented scopeExpected assessment outputs
✓ Vulnerability identification✓ Controlled security testing✓ Risk classification✓ Technical findings & reporting✓ Remediation recommendations✓ Verification & retestingNetwork infrastructure: testing coverage, methods and access are agreed before work begins.
Illustrative security workspace
Make the observations
easier to review.
This concept demonstrates how information could be presented. Actual tools, reporting and monitoring are defined in the service scope.
Illustrative dashboard
Security Risk Overview
Vulnerability trend
Sample visual / no measured customer resultsRisk distribution
Service capabilities
A practical scope.
Clear responsibilities.
Expand a capability to see how it can be considered within an agreed engagement.
01Network Vulnerability Assessment
+
Assess agreed network assets and exposed services for identifiable weaknesses.
02Web Application Security Testing
+
Review relevant application behaviours, access boundaries and configuration within the agreed scope.
03API Security Assessment
+
Assess authorised interfaces, authentication and resource access requirements.
04Server & Infrastructure Assessment
+
Review agreed hosts, services and infrastructure settings.
05Cloud Configuration Assessment
+
Assess selected cloud settings, permissions and external exposure.
06Authorised Penetration Testing
+
Validate selected weaknesses through controlled testing within documented boundaries.
07Risk-Based Security Reporting
+
Explain severity, affected assets and business context so teams can prioritise action.
08Remediation Verification
+
Retest agreed fixes and record the outcome where verification is included.
Our methodology
A structured route
from assessment to improvement.
Select a stage to explore the delivery approach.
Document asset ownership, permitted activities, exclusions, operating windows and escalation contacts.
Assessment deliverables
Technical detail.
A clear management view.
Agreed reporting connects the assessment scope and supporting observations with business context and corrective actions.
Findings reflect the assets, methods and time period reviewed. Verification and retesting are included only where agreed.
 Illustrative report structure
Security Assessment Report
Template preview / no customer findings
- 01Executive Summary
- 02Assessment Scope
- 03Findings by Severity
- 04Technical Observations
- 05Business Risk
- 06Recommended Corrective Actions
- 07Retesting Results, where applicable
Testing takes place only with the asset owner’s explicit authorisation and within a documented scope. Methods, disruption constraints, exclusions, evidence handling and retesting are agreed before work begins.
Before we begin
Clear answers for your next security step.
Can testing affect our systems?
We agree methods, operating windows and escalation contacts before testing. Potential disruption and constraints are discussed in the scope.
Is automated scanning enough?
Assessment methods depend on the objectives. Automated checks and manual validation address different questions and are scoped accordingly.
Does a test guarantee security?
No. Findings reflect the agreed scope and testing period; systems and threats change over time.
Care Via Tech Limited — Caring Via Technology.
Let’s Secure Your Digital Future.
Protect your business with security solutions aligned to your systems, operations and evolving technology needs.